
vCISO & Cyber Advisory
Board-level security leadership, pragmatic roadmaps and proportionate risk decisions without the cost of a full-time CISO.
↗ VELOXISStart a conversation
Cyber confidence at pace
Veloxis brings senior cyber, privacy and governance expertise into your organisation, turning complex risk into focused action.
Strategy that reaches
the real world.
Independent
senior expertise.
Assurance without
the theatre.
What we do
We meet organisations where they are, creating practical routes from uncertainty to control.
Board-level security leadership, pragmatic roadmaps and proportionate risk decisions without the cost of a full-time CISO.
↗Governance that turns obligations into accountable controls, useful evidence and decisions leaders can stand behind.
↗Privacy programmes designed around real data flows, clear ownership and defensible handling throughout the information lifecycle.
↗Responsible AI adoption with transparent oversight, risk classification, human accountability and practical guardrails.
↗Readiness, remediation and certification support for ISO 27001 and Cyber Essentials, focused on sustainable improvement.
↗The Veloxis approach
GDPR / NIS 2 / ISO 27001
Our people
You work with the people accountable for the advice, not a revolving delivery team.
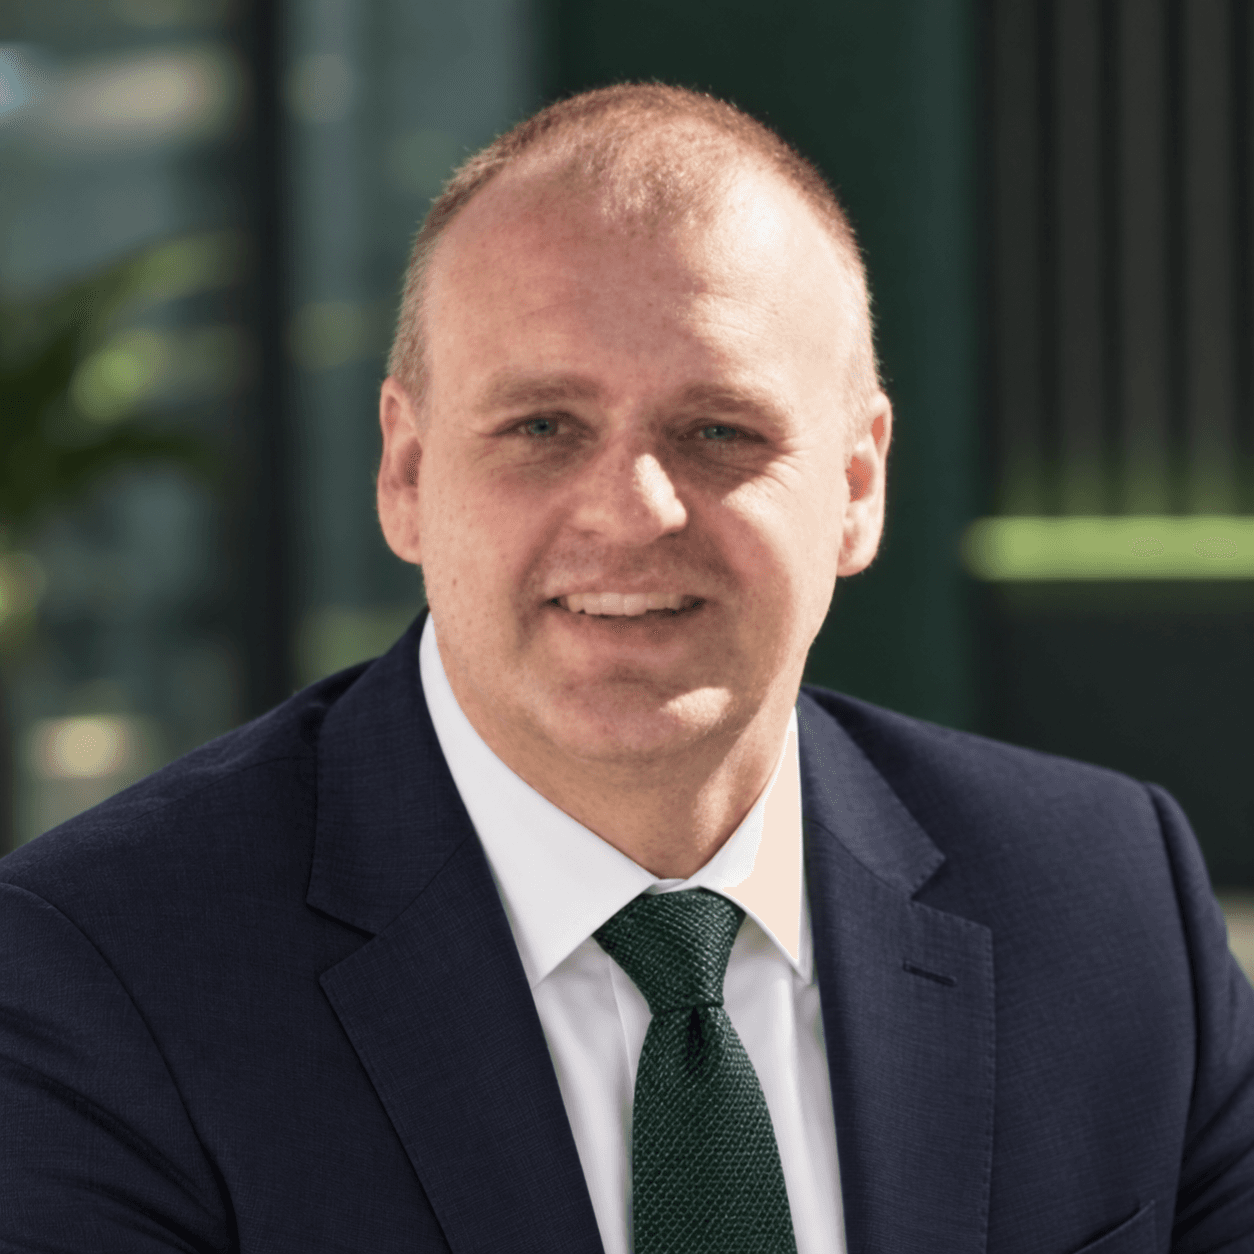
01
Darren is a cyber security leader with over three decades of experience protecting and modernising technology platforms across global and blue-chip organisations, including AXA, Pepsi Beverages Company, De La Rue and Thomson Reuters. As CTO, he has held ultimate accountability for security strategy, secure software development lifecycle practices and technology risk, embedding robust controls into complex, regulated environments. Holding SSCP, CSSLP and CISSP credentials and currently completing an MSc in Computer Science and Cybersecurity, Darren brings deep technical expertise and executive-level leadership, strengthening security posture and building high-performing teams aligned to business growth.
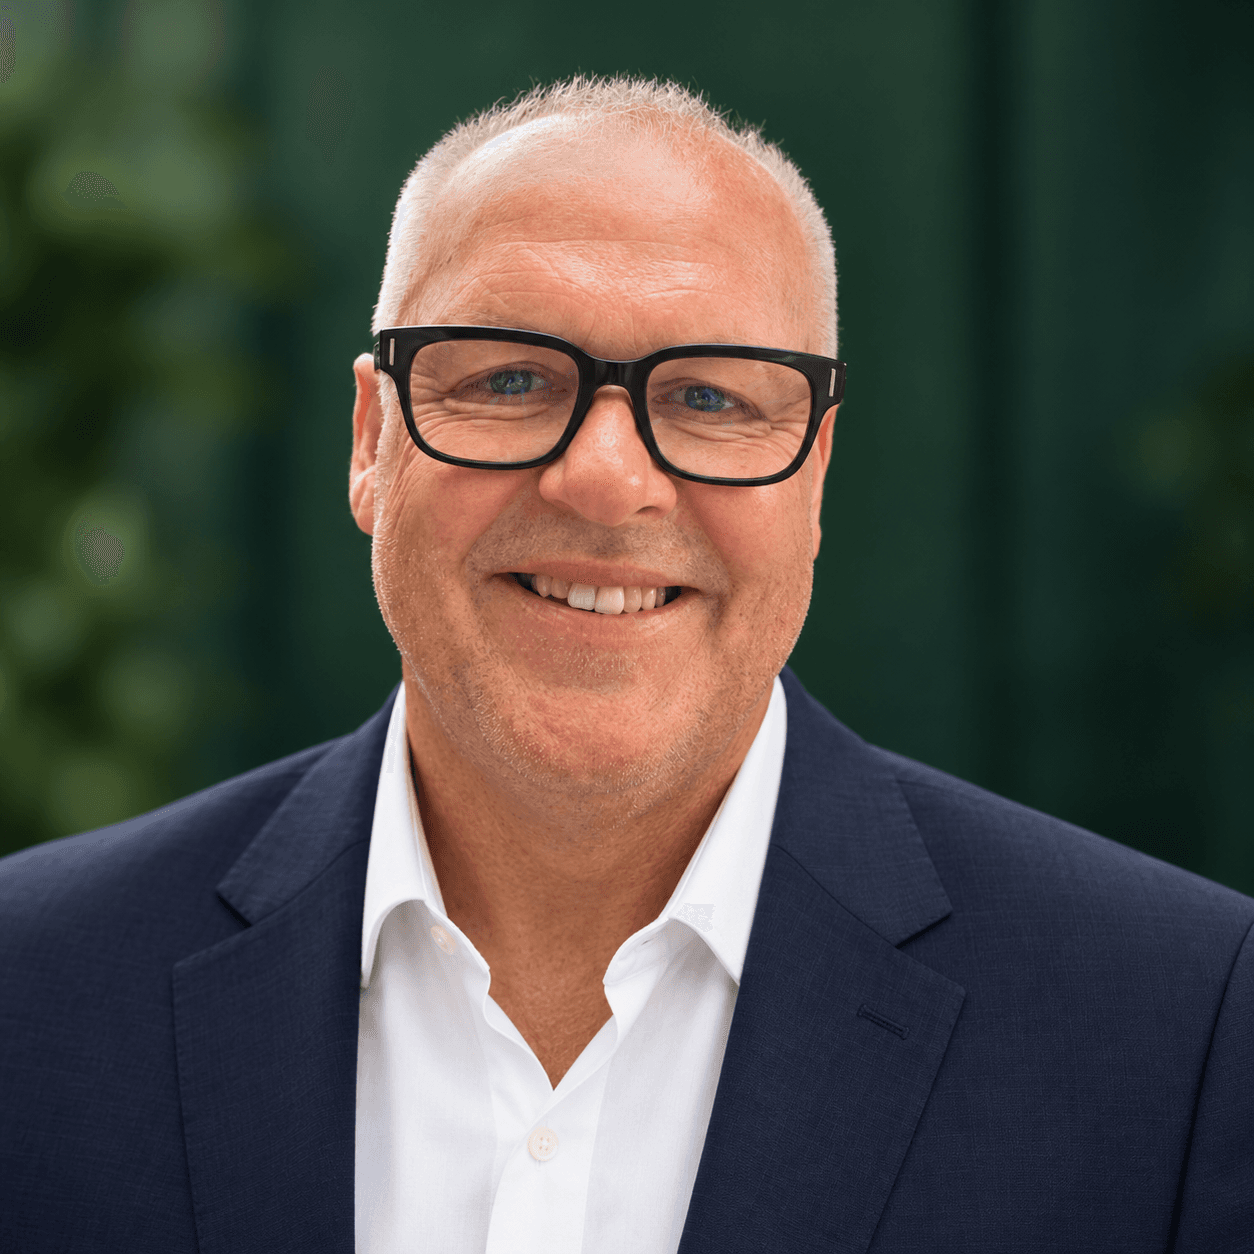
02
Bill brings over two decades of experience embedding governance, risk and privacy controls into regulated financial services environments. His track record spans global regulatory compliance, data governance and risk management, from leading FATCA, CRS and Tax Transparency compliance at HSBC to overseeing regulatory risk and data governance in complex platform integrations at Bath Building Society and beyond. Bill works closely with senior stakeholders to translate regulatory and privacy requirements into practical, well-governed delivery, combining strong analytical rigour with a clear understanding of risk to keep operations resilient, audit-ready and built on trust.
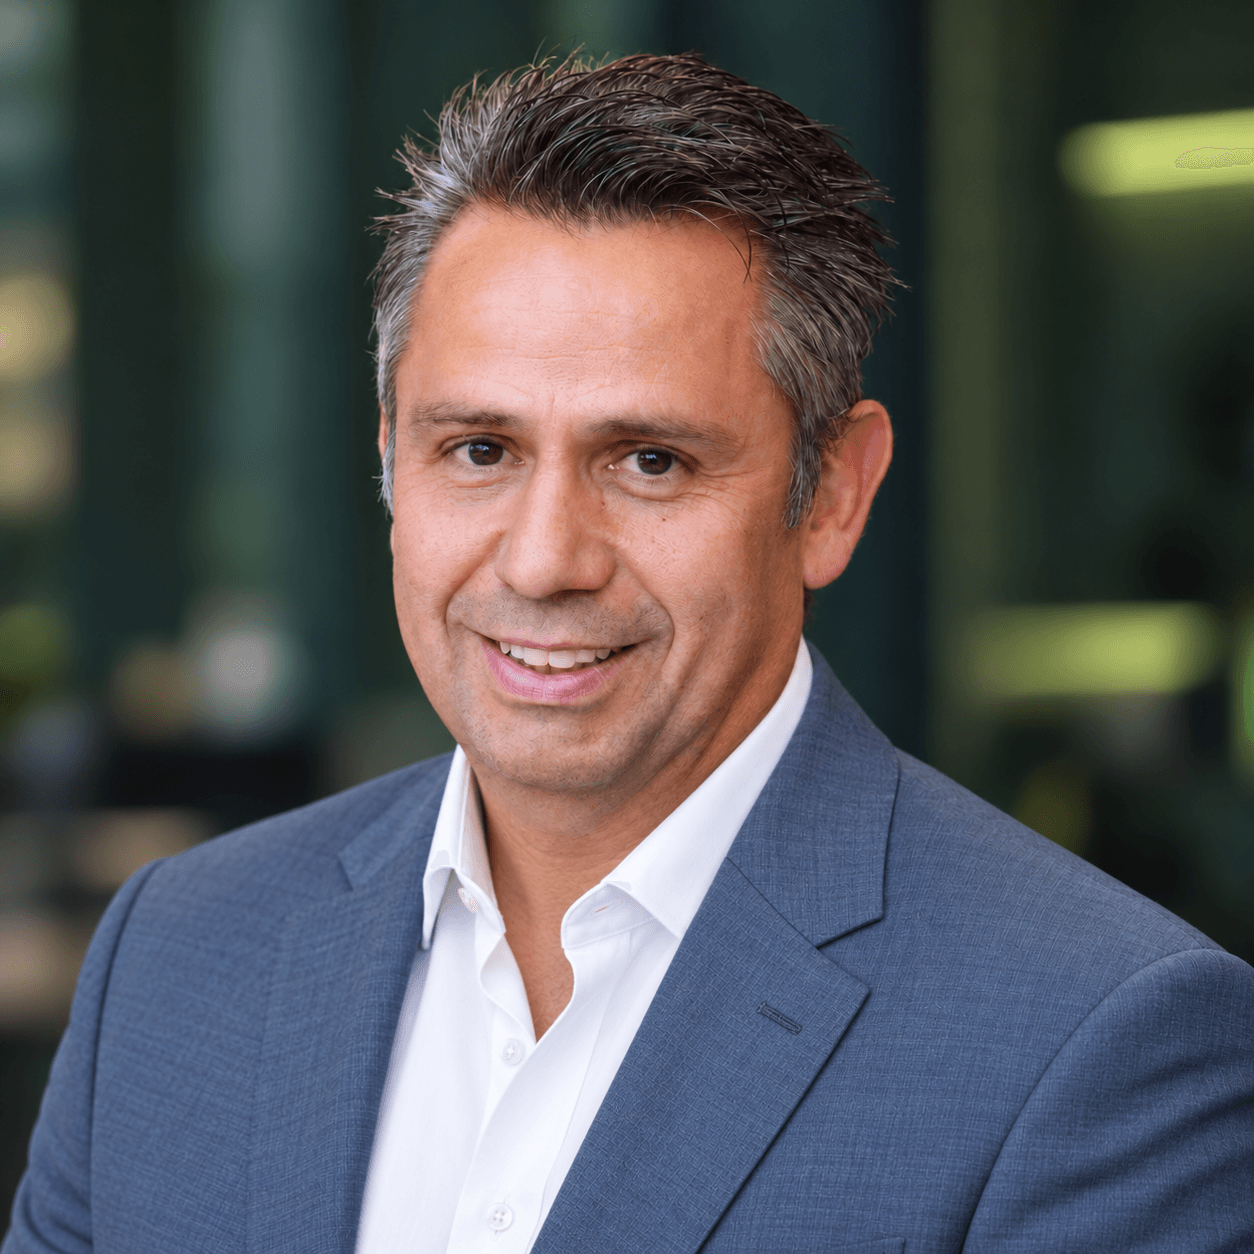
03
Neil is a cyber security and governance-focused business leader with over 20 years' international experience operating in security-critical and highly regulated environments, spanning aviation, technology, healthcare and SaaS. His recent work at Omega TSCM has centred on technical surveillance countermeasures and security risk, building on customer-facing delivery with Dubai Airports and Siemens Logistics within demanding governance frameworks central to critical national infrastructure. Neil has worked with global organisations and strategic accounts across the UK, Europe and the Middle East, including partnership development with Canon, and specialises in connecting technical, security and delivery stakeholders to shape solutions that stand up to scrutiny.
Start a conversation
Tell us briefly what you are facing. A senior advisor will respond using your chosen contact method.